CompucallWebsite security check

Sample report

For $29.99 incl. GST I test your business website the way an attacker would look at it: HTTPS, security settings, email protection (SPF, DMARC), exposed files and out-of-date software. You get the full results below, an A4 certificate with your grade, a plain-English letter listing anything to fix, and badges for your website if you score an A or B.

Order a check by email Phone 022 GOTODAV

B
Website
acme.example.com
Ended up at
https://acme.example.com/
Server address
192.0.2.10
Checked
10 Nov 2026, 10:30 am NZDT
Found
0 problem(s), 8 warning(s)

Certificate and badges
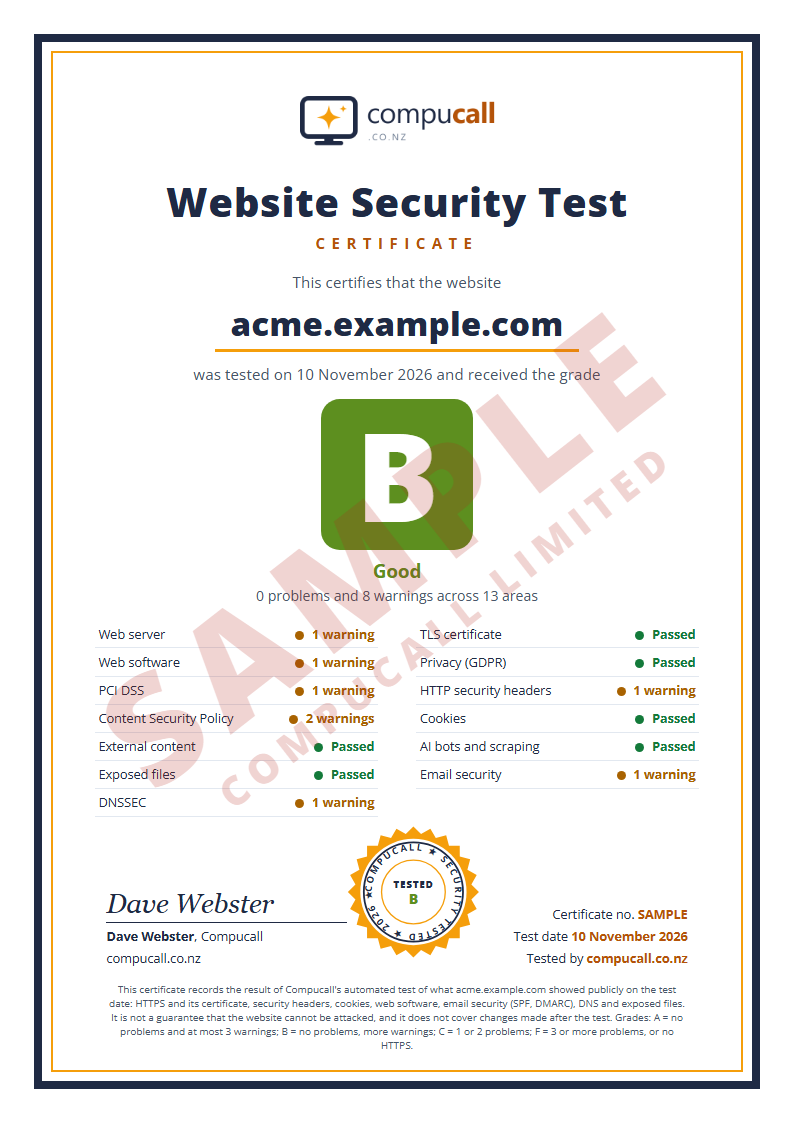
Sample A4 certificate for acme.example.com, watermarked SAMPLE, Compucall Limited

Sample dark badge, grade B, watermarked SAMPLESample light badge, grade B, watermarked SAMPLE

Sample certificate (PDF)

Your certificate and badges carry your website's name, grade and test date, without the SAMPLE watermark. Badges come with an A or B grade, in dark and light, to put on your website, email signature or marketing.

The letter that comes with it
Hello, Thank you for choosing Compucall to test the security of acme.example.com. Your website received a B grade (good) in our security test on 10 November 2026. We found 0 problems and 8 warnings. Your certificate is attached, and the points below explain what to fix, most important first. Worth fixing: - Server header shows a version: Hide version numbers so attackers cannot match known bugs. - Recognised: WordPress 6.6.2: The version is shown publicly; make sure it is the latest. - Requirement 6.4 (web firewall): No web application firewall recognised. Only matters if the site takes card payments. - Nothing stops other sites framing this one: Add X-Frame-Options: DENY or CSP frame-ancestors (clickjacking). - Content-Security-Policy is enforced but could be tighter - Scripts allow 'unsafe-inline': Injected inline scripts would run. Use nonces or hashes. - DMARC only reports (p=none): Forged mail is still delivered. Once the reports show only your own servers, change to p=quarantine, then p=reject. - DNS answers are not signed (no DNSSEC): Turn on DNSSEC at the DNS host (e.g. Cloudflare DNS > Settings) and add the DS record at the registrar. A B grade is a good result. Fixing the warnings above will take the site to an A, and the badges attached show your current grade. Most of these are settings your web developer or hosting company can change. Once they are fixed, I can re-test the site and issue an updated certificate. If you have any questions, or would like help putting these right, reply to this email or phone me on 022 468 6328. Regards, Dave Webster Compucall M 022 GOTODAV (022 468 6328) E dave@compucall.co.nz W compucall.co.nz

Web server

Good
HTTP response 200

Redirects: http://acme.example.com/ → https://acme.example.com/

Good
HTTPS works with a trusted certificate
Good
Plain http:// redirects to HTTPS

http://acme.example.com/ → https://acme.example.com/

Info
HTTP versions

Answered over HTTP/2.

Good
Compression

Supports gzip, br.

Warning
Server header shows a version

Hide version numbers so attackers cannot match known bugs.

Server: Apache/2.4.58 (Ubuntu)
Info
No firewall or CDN recognised
Info
HTTP methods

Allow: GET, HEAD, POST, OPTIONS

TLS certificate

Good
Certificate valid for 71 more days

Issued by Let's Encrypt (R11) for acme.example.com, www.acme.example.com

Good
Connection uses TLSv1.3

TLS_AES_256_GCM_SHA384

Good
TLS 1.0 and 1.1 are refused
Info
No CAA record

Optional: a CAA record in DNS names the only certificate authorities allowed to issue certificates for this domain.

Web software

Warning
Recognised: WordPress 6.6.2

The version is shown publicly; make sure it is the latest.

Privacy (GDPR)

Good
A privacy policy is linked

https://acme.example.com/privacy-policy/

Good
Pages are encrypted (HTTPS)
Good
No tracking cookies on the first visit

PCI DSS

Good
Requirement 6.3 (known holes)

No outdated software was recognised.

Warning
Requirement 6.4 (web firewall)

No web application firewall recognised. Only matters if the site takes card payments.

HTTP security headers

Good
Strict-Transport-Security is set
Strict-Transport-Security: max-age=31536000
Good
X-Content-Type-Options
X-Content-Type-Options: nosniff
Warning
Nothing stops other sites framing this one

Add X-Frame-Options: DENY or CSP frame-ancestors (clickjacking).

Good
Referrer-Policy
Referrer-Policy: strict-origin-when-cross-origin
Info
Permissions-Policy

Missing (optional): it switches off camera, microphone, etc. for the page.

Content Security Policy

Warning
Content-Security-Policy is enforced but could be tighter
Content-Security-Policy: default-src 'self'; script-src 'self' 'unsafe-inline'; img-src 'self' data:
Warning
Scripts allow 'unsafe-inline'

Injected inline scripts would run. Use nonces or hashes.

Info
No base-uri

Add base-uri 'none' or 'self'.

Cookies

Good
No cookies were set on the first visit

External content

Info
3 outside file(s) from 2 site(s)

fonts.googleapis.com, fonts.gstatic.com. Each one learns your visitors' IP addresses.

AI bots and scraping

Info
robots.txt blocks 0 of 13 AI crawlers

robots.txt is a request; well-behaved bots follow it.

Exposed files

Good
No common leaked files found

Checked 10 paths that often give away code, passwords or backups.

Info
No security.txt

Optional: /.well-known/security.txt tells people who find a problem how to report it (RFC 9116).

Email security

Info
acme.example.com receives email
10 mx1.mail.example.net.
20 mx2.mail.example.net.
Good
SPF is set (~all)
v=spf1 include:_spf.mail.example.net ~all
Warning
DMARC only reports (p=none)

Forged mail is still delivered. Once the reports show only your own servers, change to p=quarantine, then p=reject.

v=DMARC1; p=none; rua=mailto:dmarc@acme.example.com
Good
DKIM key found (selector1)
Info
No MTA-STS

Optional: MTA-STS makes other mail servers use encrypted, checked connections when sending to you.

DNSSEC

Warning
DNS answers are not signed (no DNSSEC)

Turn on DNSSEC at the DNS host (e.g. Cloudflare DNS > Settings) and add the DS record at the registrar.